

Statement: Customers need clear guidelines and a far higher budget for cyber protection. From NIS2 to GDPR, from the EU AI Act to ISO27001 — Europe’s regulatory storm keeps growing.
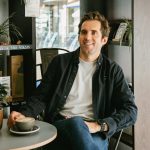
For large enterprises, compliance is a headache; for SMEs and public institutions, it’s paralysis. In this interview, Mixvoip’s CEO, Loic Didelot explains why regulation without clarity is crushing smaller organisations, and how smarter guidance — not more consultants — could finally make Europe safer.
There’s been an avalanche of regulations — NIS2, DORA, CRA, GDPR, the EU AI Act, ISO27001. How on earth can an SME or a municipality navigate this maze without going broke on consultants?
L.D. Honestly, they can’t — not without help. Each regulation was written with good intent, but together they form a maze that even large companies struggle to navigate. SMEs, municipalities, public associations and schools don’t have compliance teams or the time to decode hundreds of pages of EU text. Hiring consultants fixes the symptoms, not the cause. What’s really missing are clear, practical national guidelines that translate laws into simple steps. If governments published easy-to-follow rules — what’s mandatory, what’s recommended, what’s overkill — IT providers could apply them directly and guide their customers without endless consulting. That would save money, time, and a lot of frustration.
“The problem is that most companies still invest more in protecting their buildings than their data.”
Loïc Didelot, CEO of Mixvoip
You say governments should publish clearer, more practical guidelines. What kind of guidance do you have in mind?
L.D. Something concrete. A framework that answers the basic, real-life questions every IT manager or mayor faces. When should you buy DDoS protection? When do you need MDM (mobile device management)? Should your firewall be managed by the same company that runs everything else? When does a small commune need a SOC-as-a-service, or tools like SIEM, XDR, or brand-monitoring against phishing? There are too many acronyms and not enough direction. Governments don’t have to dictate every detail, but they should publish checklists and examples by size and risk level. We don’t want to sell customers what they don’t need but cyber can’t stay buried inside the general IT budget. It deserves its own line, its own strategy, and clear national benchmarks.
Some might say your message just means “spend more on cybersecurity”. Isn’t this simply a way for providers like you to sell more services?
L.D. Yes, it’s very convenient but it’s also true. The problem is that most companies still invest more in protecting their buildings than their data. They have cameras, alarms, and access control because insurers demand it. You can’t insure your office if you leave the door open. Yet when it comes to data, the real core of most organisations, there’s no equivalent standard, no inspection, no culture of prevention.
Cyber threats are still relatively new, not brand new, but growing faster every year. The attacks are more automated, more targeted, and increasingly aimed at small and public organisations. So yes, budgets have to follow. Unfortunately.
At the end of the day, it’s simple: if your data isn’t important, don’t protect it. You don’t install prison-grade security for a house full of cutlery and one flat screen. But every business should ask: what happens if our data is gone, or if we’re offline for a week? In most cases, the answer is the same. You’re out of business. That’s why budgets must follow the real risk, not the visible one.
“Our cyber team is there to guide customers, but our main goal is to build as much protection as possible directly into our products”
Loïc Didelot, CEO of Mixvoip
After all this, regulations, risks, and budget pressure, what does Mixvoip actually do to help customers protect themselves?
L.D. Our cyber team is there to guide customers, but our main goal is to build as much protection as possible directly into our products and make it affordable. We work to make them accessible to everyone.
For example, our DNS Shield is included by default with every internet contract at no extra cost. We also keep our DDoS protection on the lower end of the pricing scale so even small organisations can afford it. For mobile device management, we provide an alternative to Microsoft that reduces costs significantly.
Our telephony services have included a free anti-fraud system for more than 12 years, even when customers use phone systems that are not managed by us. If a customer is hacked, they don’t pay the damage, which means we’ve invested heavily in protection, monitoring, and our own source code.
Next on our roadmap are free cybersecurity consulting sessions. AMA (Ask Me Anything) style exchanges where customers can get honest answers and practical advice without fear of being upsold.